The OpenClaw Paradox: Hype in China, Caution in Policy and What It Means for AI Governance
China is not rejecting AI agents, but it is making clear that agent deployment must be controlled like a high-risk operational system, not treated like an ordinary chatbot tool.
When agents stop answering and start acting
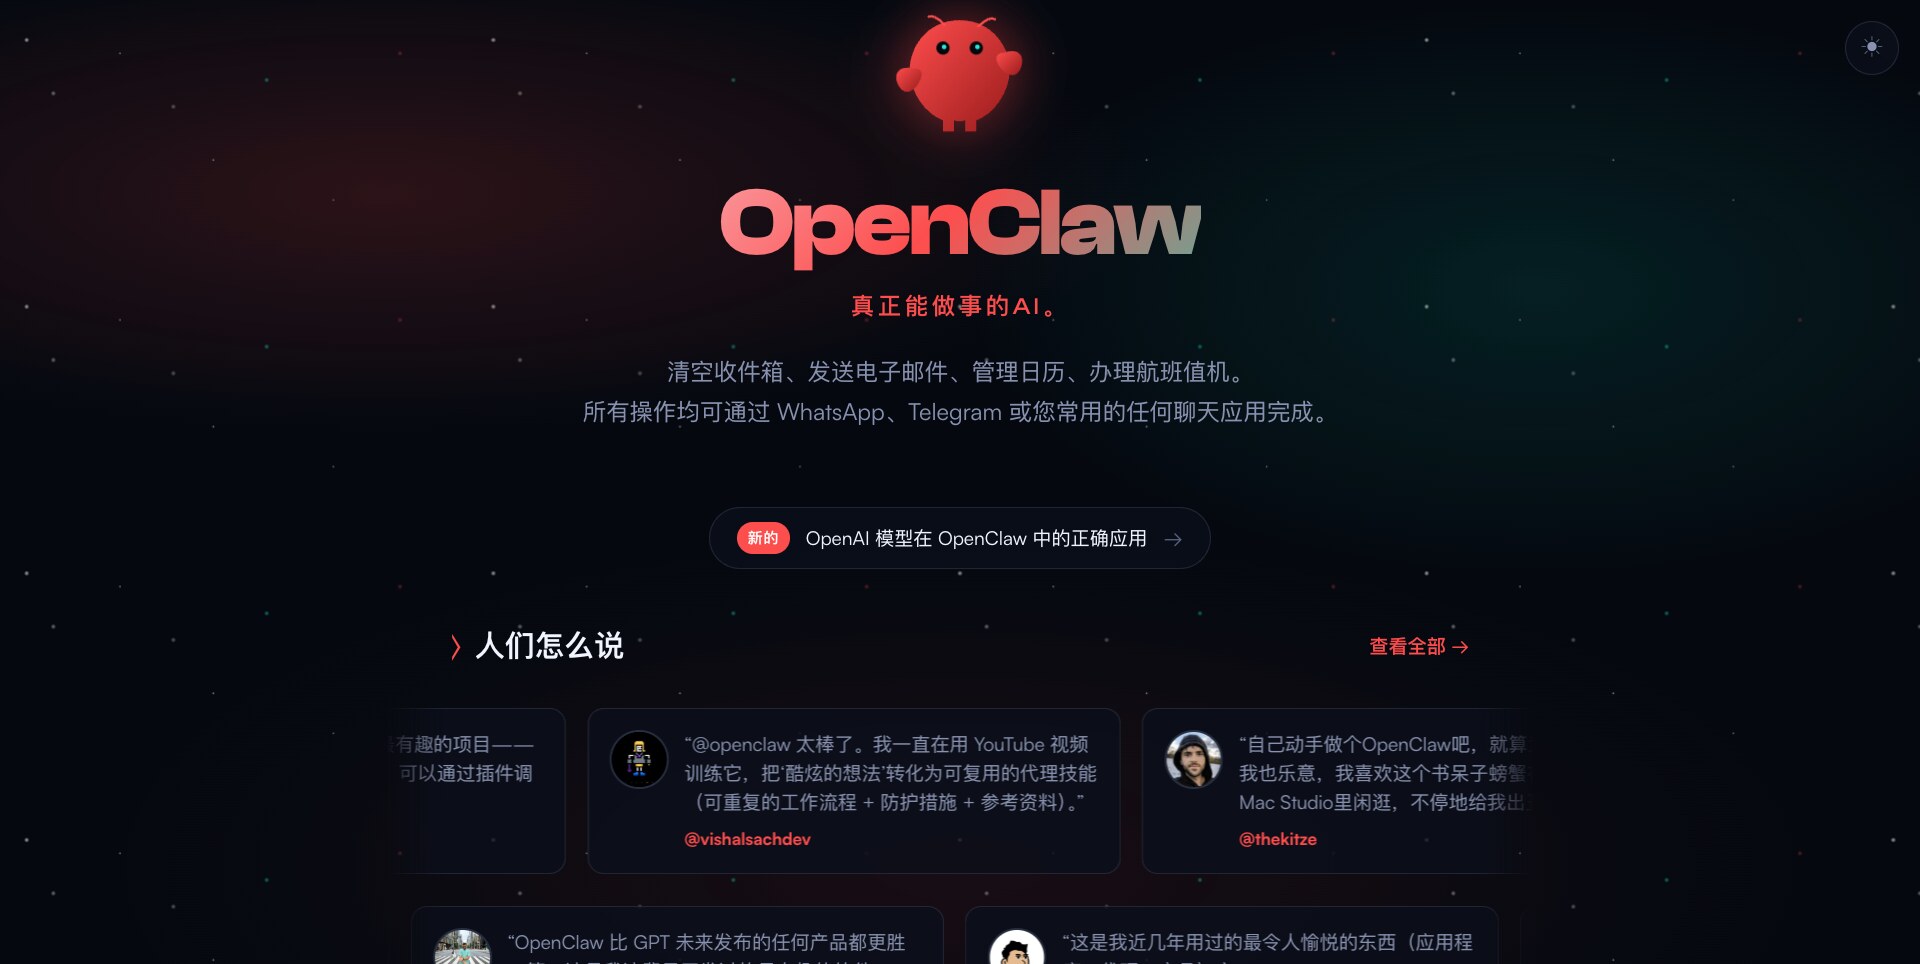
What happens when an AI tool stops answering questions and starts taking action on its own? That is the real concern around the rapid rise in the use of OpenClaw in China. Official Chinese state security reports estimate that there are more than 200,000 active OpenClaw internet assets globally, including around 23,000 in China alone.
Much of the public discussion has focused on speed, automation and productivity. But recent guidance from Chinese authorities is steering users in a different direction. The message is not that AI agents should be avoided. It is that once an agent can access files, leverage system tools and act across systems, it creates a different level of risk. At that point, it should no longer be treated like an ordinary chatbot, but as a high-risk operational system that needs clear controls, limited permissions and ongoing oversight.
What China's March 2026 advisory said
China's policy signal has been much more cautious than the market excitement. In March 2026, the MIIT-run National Vulnerability Database issued a "six dos and six don'ts" style advisory for OpenClaw users. The guidance did not frame the tool as an ordinary productivity assistant. Instead, it focused on operational safeguards such as:
- Using the latest official version
- Limiting internet exposure
- Applying least privilege
- Using third-party skill markets carefully
- Guarding against browser hijacking
- Checking regularly for security patches
Users were also warned not to expose instances directly to the internet, not to deploy with administrator accounts, and not to disable detailed log auditing.
A second wave of operational guidance
That message became even clearer in the next wave of guidance. China's security alerts described risks not only in OpenClaw's default configuration and vulnerability management, but also in its plugin ecosystem and behaviour control mechanisms. State media reporting on the later CNCERT and Cyber Security Association guidance said individual users should run OpenClaw only on dedicated devices, virtual machines or containers, avoid administrator privileges, and keep sensitive personal data out of the OpenClaw environment.
The more technical recommendations went further, covering IP allowlisting (also known as white-listing), VPN-only remote access, detailed logging, strict filesystem controls, third-party skill review, cloud IAM (Identity and Access Management) controls, supply chain checks and stronger data protection in cloud deployments.
Why this matters for AI governance
This is why the OpenClaw story matters for AI governance. China is not rejecting AI agents. It is recognising that once a model can take actions, call tools, interact with external systems and operate with elevated permissions, the governance question changes. The issue is no longer only whether an answer is wrong. It is whether an agent can delete files, leak credentials, misuse permissions or trigger wider system disruption. That is much closer to operational risk than to ordinary chatbot risk.
Treating agentic AI as a governance question
The wider issue is one of effective guardrailing. As AI tools move from generating content to taking action, governance must move with them. Businesses should not assess agentic AI only through an innovation lens. They should also look carefully at access rights, system boundaries, monitoring, human checkpoints and incident response.
In practice, that means treating deployment as a governance issue from the start, not as a technical experiment to fix later. Where agents may interact with sensitive data or critical systems, early input from privacy, legal and security professionals will often be essential.